AI Tools in the Workplace: What Businesses Should Consider Before Giving Them Access to Company Data
This is especially timely because businesses are rapidly adopting AI tools, while employees may not realise what they are authorising when they connect an AI application to Microsoft 365.
AI Tools in the Workplace: What Businesses Should Consider Before Giving Them Access to Company Data
Artificial intelligence tools are rapidly becoming part of everyday business.
Employees are using AI to draft emails, summarise documents, analyse information, prepare reports and automate repetitive tasks.
Used appropriately, these tools can provide significant productivity benefits.
But there’s an important question businesses should ask before connecting an AI application to Microsoft 365:
What information are we giving it access to?
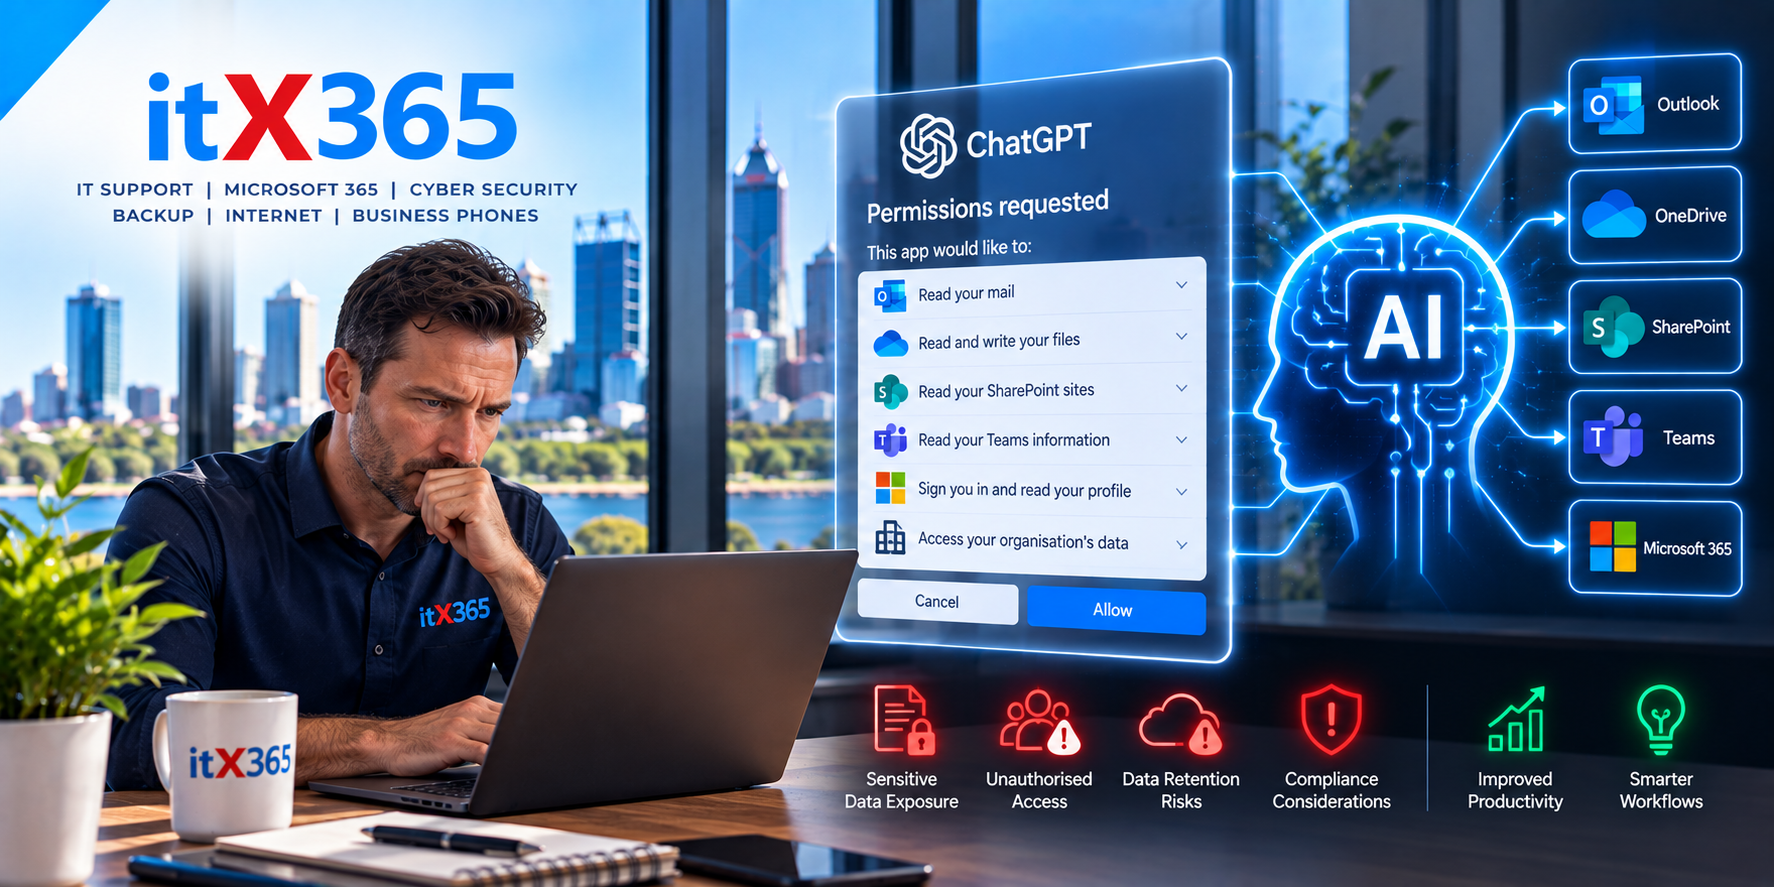
Clicking Allow on a permissions screen can potentially provide an application with access to much more company information than an employee realises.
That doesn’t mean businesses should avoid AI.
It means AI adoption should be managed in the same way as any other technology that handles company information.
Not all AI tools are the same
The term “AI” covers an enormous range of products.
Some AI tools operate as standalone websites where an employee manually enters information.
Others install applications on computers.
Some integrate directly with Microsoft 365.
Others connect to SharePoint, OneDrive, email, calendars, CRM platforms or other business systems.
These are very different risk scenarios.
The important question isn’t simply:
“Do we allow AI?”
A better question is:
“What does this particular application do, and what information does it need access to?”
Pay attention to Microsoft 365 permissions
When an application integrates with Microsoft 365, it may request permissions to access company information.
Depending on the application and permissions requested, this could potentially include access to things such as:
- User profiles
- Calendars
- OneDrive files
- SharePoint data
- Teams information
- Company directory information
Some applications only require limited access.
Others may request considerably broader permissions.
Before approving an application, businesses should understand what is being requested and why.
“Sign in with Microsoft” doesn’t mean Microsoft made the application
This is an important distinction.
Many third-party applications allow users to sign in using their Microsoft account.
That can be convenient and may provide secure authentication.
However, seeing a Microsoft login screen doesn’t necessarily mean the application itself is a Microsoft product or has been approved by Microsoft for your organisation.
The login process identifies the user.
The permissions requested afterwards determine what the application may be able to access.
Employees should therefore avoid treating every Sign in with Microsoft button as automatic approval to connect a service to company information.
The principle of least privilege applies to AI too
A useful cybersecurity principle is least privilege.
Users and applications should only receive the access they actually require.
For example, if an AI application only needs access to a specific set of documents, does it really need access to every SharePoint site in the organisation?
If it only needs to help draft text, does it need access to company email?
If the requested permissions seem much broader than the function being provided, that’s worth investigating.
Giving applications unnecessary access increases the potential impact if something goes wrong.
Where does your information go?
Before providing sensitive business information to an AI service, organisations should understand how that information is handled.
Useful questions include:
Is the information retained?
Where is it stored?
How long is it retained?
Is it used to improve or train models?
Can administrators control retention?
Can the information be deleted?
Where is the service hosted?
What happens when an employee leaves the business?
The answers will vary significantly between providers and between consumer and business versions of the same service.
Free and consumer AI accounts deserve particular attention
Employees may discover useful AI tools independently and create accounts using their company email address.
This can create what is sometimes called shadow IT — technology being used for business purposes without the organisation necessarily knowing about or managing it.
The problem isn’t that every free AI tool is unsafe.
The problem is that the business may have no visibility into what company information is being entered, where that information is going or whether access can be removed later.
For sensitive business information, organisations should consider whether an approved business-grade service is more appropriate.
Be especially careful with sensitive information
Not all business information carries the same risk.
Asking an AI tool to improve the wording of a generic marketing paragraph is very different from uploading confidential client documents.
Businesses should think carefully before providing AI systems with information such as:
- Customer records
- Legal documents
- Financial information
- Employee information
- Passwords or credentials
- Confidential correspondence
- Contracts
- Personally identifiable information
- Proprietary business information
Some industries may also have contractual, regulatory or professional obligations governing how information can be handled.
AI applications can create another path into company data
Cybersecurity traditionally focuses on users, computers and networks.
Cloud applications have added another consideration: application access.
Even if an employee has strong MFA and a properly secured computer, a third-party application that has been granted access to their Microsoft 365 information creates another relationship that needs to be considered.
That doesn’t automatically make the application dangerous.
But it does mean application permissions should form part of the organisation’s security management.
Administrator access requires even greater caution
Requests for administrator permissions should receive particular scrutiny.
Administrative accounts can potentially access or change significant parts of an organisation’s Microsoft 365 environment.
Providing an application with broad administrative permissions can therefore carry considerably more risk than allowing an ordinary user to sign in.
Before granting administrator access, businesses should understand exactly what permissions are being requested and whether they are genuinely required.
Convenience shouldn’t be the deciding factor.
Create an AI policy before you need one
Businesses don’t necessarily need a 40-page AI policy.
For many small organisations, a few clear rules can make a significant difference.
For example:
- Which AI services are approved?
- Can employees use company information with AI tools?
- What information must never be uploaded?
- Who can approve new AI applications?
- Who can approve Microsoft 365 integrations?
- Are free consumer AI accounts permitted?
- What happens when an employee leaves?
- Who reviews application permissions?
The goal shouldn’t be to prevent employees from benefiting from AI.
It’s to establish reasonable boundaries.
AI security shouldn’t become AI prohibition
There is a danger of approaching AI entirely from a security perspective.
Businesses that prohibit every AI tool may miss genuine productivity opportunities — and employees may simply start using unapproved services instead.
A better approach is to evaluate the business requirement and then find an appropriate way to meet it.
Ask:
What is the employee trying to achieve?
There may be an approved AI platform that provides the required capability while giving the organisation better control over its information.
Security works best when it enables the business rather than simply saying no.
Review connected applications regularly
Application access shouldn’t be treated as permanent.
Over time, employees leave, projects finish and applications stop being used.
Businesses should periodically review which applications have access to their environment and remove permissions that are no longer required.
This principle applies to AI applications as well as traditional cloud software.
AI should become part of your broader cybersecurity strategy
AI isn’t a completely separate security problem.
It fits into many of the same principles businesses should already be applying:
- Multi-Factor Authentication
- Least privilege
- Device management
- Data protection
- User awareness
- Application control
- Administrator security
- Monitoring
- Backup and recovery
As AI becomes more deeply integrated into business applications, these controls will become even more important.
Helping businesses adopt AI safely
At itX365, we believe businesses should be able to benefit from new technology without unnecessarily exposing company information.
When an application requests access to Microsoft 365, the question shouldn’t simply be whether the software is useful.
We also need to understand what it can access, what permissions it requires and how that fits into the organisation’s overall security environment.
For businesses using Microsoft 365, this can form part of a broader managed IT and cybersecurity strategy.
Before you click “Allow”
The next time an AI application asks for access to your company’s Microsoft 365 environment, take a moment to look at what it’s requesting.
If you’re unsure what those permissions mean, ask before approving them.
A five-minute security review is considerably easier than investigating a data-security problem afterwards.
Talk to itX365 if you’d like help reviewing Microsoft 365 application permissions or developing practical guidelines for the use of AI within your business.